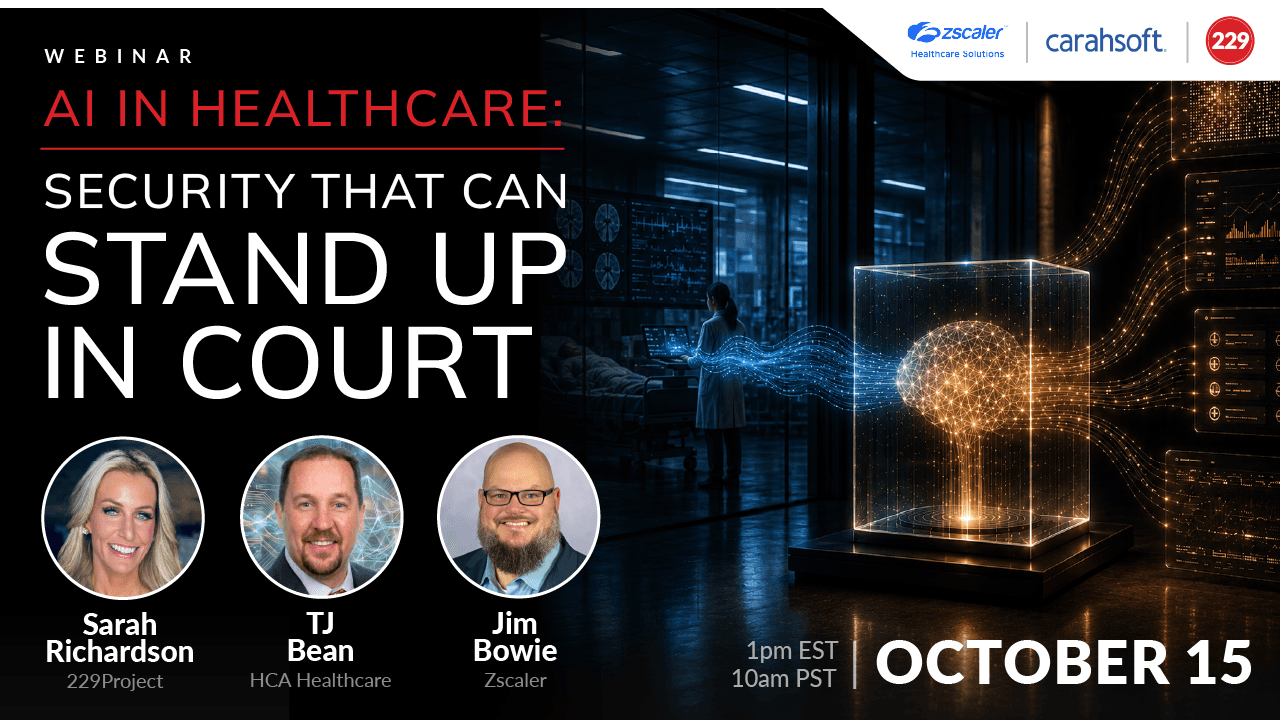
AI is already embedded in clinical and operational workflows, including ambient documentation, decision support, scheduling, and analytics.
Can you defend it?
The question for healthcare executives is no longer whether they will use AI. It is whether the organization can defend how it was used when something goes wrong.
Visibility alone is not enough. Leaders need to know who can use which AI tools, what controls govern that use, and whether they can reconstruct what the AI did when a patient safety event or legal claim is investigated.
In this session TJ Bean, VP of Information Security at HCA Healthcare, joins Jim Bowie of Zscaler, formerly VP and CISO at Tampa General, to discuss:
Identity and authorization for AI tools
Isolating AI workloads from core clinical systems
Building the audit trail regulators and courts may expect
Built for leaders who already have AI in production and need to prove it is governed, not just running.


Sponsored by